What Is Two-Factor Authentication Backup and Why Does It Matter?
Understanding two-factor authentication backup and why does it matter is essential for anyone who relies on digital accounts to manage their daily life. While standard security measures like passwords are a good start, they are rarely enough to stop determined attackers on their own. By adding a secondary layer of verification, you create a safety net that protects your personal data from unauthorized access.
This article explains how these recovery mechanisms function and why they are the most critical component of your online identity protection. You will learn how to set them up properly so that you never find yourself locked out of your own digital world.
Defining the Role of Authentication Recovery
Two-factor authentication backup refers to the secondary methods provided by service platforms to regain entry when your primary verification device is missing or inaccessible. Many users mistakenly believe that enabling two-factor authentication is the final step in securing an account.
In reality, the moment you activate this feature, you become entirely dependent on a single piece of hardware, such as a smartphone. If that device is lost, stolen, or damaged, you face an immediate crisis regarding your digital access.
Recovery methods serve as the “break-glass” procedure for these scenarios. They ensure that you retain control over your accounts even when the standard authenticator app or SMS verification fails.
Without these backups, a simple hardware failure can result in permanent loss of access to email, banking, or social media profiles. The backup process is the bridge between a locked-out state and full account restoration.
The Mechanics of Recovery Codes
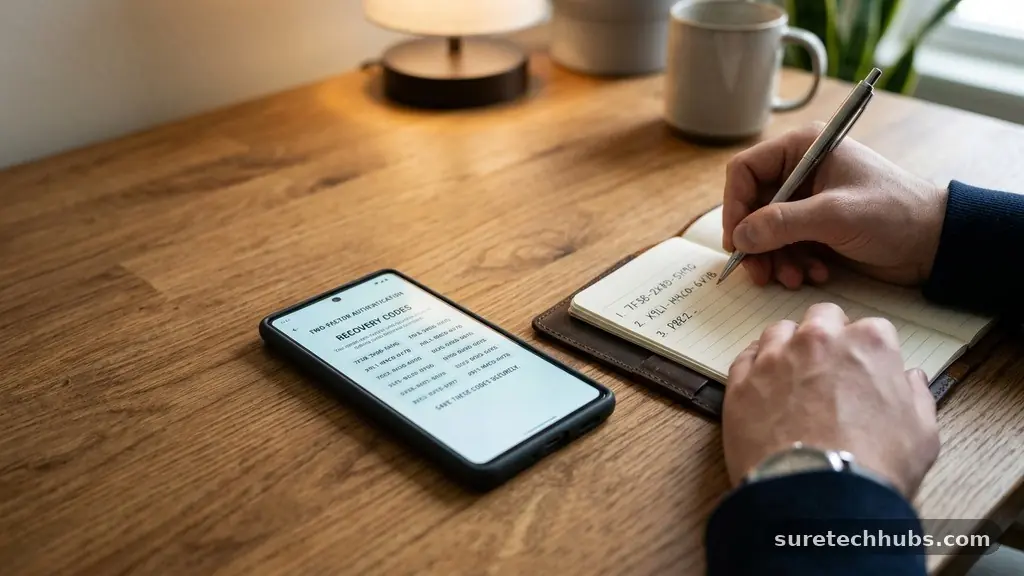
The most common form of backup is a set of unique, one-time-use alphanumeric strings known as backup codes. When you first enable two-factor authentication on a platform, the service typically generates a list of these codes for you to save in a secure location.
Each code acts as a master key that bypasses the need for your primary authenticator app. Once you use a specific code, it is invalidated, preventing anyone else from using it in the future.
These codes are designed to be printed or stored offline, away from the device they protect. If you lose your phone, you simply retrieve your stored list, enter one of the remaining codes, and regain access to your settings.
This system is highly effective because it does not rely on cellular networks or internet connectivity. It is a purely manual, physical security measure that remains functional under almost any circumstance.
Why Your Access Depends on Redundancy
Redundancy is the cornerstone of modern security architecture. If your security strategy has a single point of failure, that point will eventually be exploited or compromised.
By relying solely on one device for verification, you are inviting a situation where a dead battery or a broken screen prevents you from logging in. A robust security setup requires at least two distinct paths to prove your identity.
This is exactly why two-factor authentication backup and why does it matter becomes a central question for every user. When you have a backup, you eliminate the risk of being permanently sidelined by technical glitches.
It transforms a potential disaster into a minor inconvenience. Maintaining multiple recovery options ensures that your access remains fluid and under your direct control at all times.
Comparing Common Recovery Methods
Not all recovery methods are created equal, and different platforms offer varying degrees of security. Some services allow you to register a secondary email address for account recovery, while others rely strictly on printed codes.
It is important to understand the hierarchy of these methods to choose the most secure path. You can find detailed information on best practices through the Cybersecurity and Infrastructure Security Agency.
The following table compares the efficacy and risk profiles of standard recovery methods available to the average user.
| Method | Accessibility | Security Level | Primary Risk |
|---|---|---|---|
| Printable Codes | High | High | Physical loss of paper |
| Secondary Email | Medium | Low | Email account compromise |
| SMS Recovery | High | Low | SIM swapping attacks |
| Hardware Keys | Low | Very High | Physical loss of key |
Managing Devices and Security Keys
Beyond simple codes, many users now utilize physical security keys or secondary devices to manage their authentication. A security key is a small USB or NFC device that acts as a physical token for verification.
These are significantly more secure than SMS or email backups because they cannot be intercepted remotely. However, they introduce the risk of physical loss, requiring you to have a backup key registered to the same account.
If you choose to use a secondary device, such as a tablet or a work computer, you must ensure that those devices are also protected. An authenticated device is essentially a bypass for your security.
If that device is stolen, the thief could potentially access your accounts. Always keep your recovery hardware in a location that is physically separate from your primary computer or phone.
Steps for Protecting Your Recovery Assets
Once you have generated your backup codes, the way you store them is just as important as the security of the account itself. Many people make the mistake of saving these codes in a text file on their desktop or in an unencrypted cloud folder.
If an attacker gains access to your computer, they will find those files immediately. You should treat these codes with the same level of care you would give a passport or a birth certificate.
- Print your codes and store them in a fireproof safe or a locked cabinet.
- Use a dedicated, encrypted password manager to store digital copies of codes.
- Never take a simple screenshot of your codes, as these are often synced to cloud photo galleries.
- Periodically review which devices have current access to your accounts.
- Update your recovery information whenever you change your primary phone number.
Frequently Asked Questions
What happens if I lose my backup codes?
If you lose your backup codes and no longer have access to your primary authenticator, you must use the platform’s account recovery process. This usually involves answering security questions or providing government-issued ID to prove your identity. This process can take several days and is often stressful, which is why keeping your codes safe is vital.
Is it safe to store backup codes in a password manager?
Yes, storing codes in a reputable, encrypted password manager is generally safe and recommended. Password managers use advanced encryption standards that keep your data private even if the device is compromised. Just ensure that your master password is strong and that you have enabled two-factor authentication on the password manager account itself.
Can I use a friend’s phone number as a backup?
While some platforms allow you to add a secondary phone number, it is generally discouraged to use a friend’s number. If there is a dispute or a falling out, you could lose access to your account permanently. Only use phone numbers or recovery addresses that you personally control and will maintain access to for the long term.
Are backup codes the same as recovery emails?
No, they are distinct. Recovery emails are a mechanism where a platform sends a link to an external address to reset your login. Backup codes are specific, pre-generated strings that you enter during the login process to bypass the need for an authenticator app. Codes provide a much higher level of security than email-based resets.
Do backup codes expire?
In most cases, backup codes do not expire until they are used. Once a code is used, it is typically discarded by the system. It is good practice to generate a new set of codes if you suspect that your existing list has been viewed by someone else or if you have used more than half of the available entries.
Securing Your Future Digital Presence
Taking the time to understand two-factor authentication backup and why does it matter is a proactive step toward digital maturity. By acknowledging that technology can fail, you protect yourself against the unexpected loss of your most valuable accounts. Whether you use printed codes, a secure password manager, or a physical hardware key, the goal is always to maintain multiple paths for identity verification.
Start today by logging into your most important accounts and checking your security settings. Ensure that you have generated and safely stored your recovery codes, and remove any outdated devices from your account access lists.
This small investment of time will pay dividends in peace of mind. Your digital identity is worth the effort, and your future self will appreciate the preparation you put into securing your access today.